TUN
tun:  enable: true  stack: mips  auto-route: true  auto-redirect: true  auto-detect-interface: true  # dns-mode: hijack  dns-hijack:    - any:53    - tcp://any:53  device: utun0  mtu: 9000  strict-route: true  gso: true  gso-max-size: 65536  inet6-address: [fdfe:dcba:9876::1/126]  udp-timeout: 300  iproute2-table-index: 2022  iproute2-rule-index: 9000  endpoint-independent-nat: false  route-address-set:    - ruleset-1  route-exclude-address-set:    - ruleset-2  route-address:    - 0.0.0.0/1    - 128.0.0.0/1    - "::/1"    - "8000::/1"  route-exclude-address:  - 192.168.0.0/16  - fc00::/7  include-interface:  - eth0  exclude-interface:  - eth1  include-uid:  - 0  include-uid-range:  - 1000:9999  exclude-uid:  - 1000  exclude-uid-range:  - 1000:9999  include-mac-address:  - 00:11:22:33:44:55  exclude-mac-address:  - 00:11:22:33:44:66  include-android-user:  - 0  - 10  include-package:  - com.android.chrome  exclude-package:  - com.android.captiveportallogin
## Legacy Syntax  inet4-route-address:  - 0.0.0.0/1  - 128.0.0.0/1  inet6-route-address:  - "::/1"  - "8000::/1"  inet4-route-exclude-address:  - 192.168.0.0/16  inet6-route-exclude-address:  - fc00::/7
enable
Section titled “enable”Enable TUN mode.
TUN mode protocol stack. If no usage issues occur, mips stack is recommended. Default is mips.
Available values: system/gvisor/mixed/mips
device
Section titled “device”Specify the name of the TUN network interface. MacOS devices can only use interface names starting with utun.
auto-route
Section titled “auto-route”Automatically set global routes, which can automatically route global traffic into the TUN network interface.
auto-redirect
Section titled “auto-redirect”Linux only. Automatically configures iptables/nftables to redirect TCP connections. Requires auto-route to be enabled.
On Android:
Only forwards local IPv4 connections. To share your VPN connection via hotspot or tethering, please use VPNHotspot.
On Linux:
With auto-route enabled, auto-redirect now works on routers as expected without any manual intervention.
auto-detect-interface
Section titled “auto-detect-interface”Automatically detect the outbound interface for traffic. It is recommended to manually specify the outbound network interface for devices connected to multiple outbound interfaces simultaneously.
dns-mode
Section titled “dns-mode”How the system DNS is configured
disableddoes not set the system DNSnativesets the tun address as the system DNShijackadditionally intercepts traffic sent to port 53 of other interfaces on top ofnative(requiresstrict-routeon Windows andauto-redirecton Linux)- If left empty, the legacy behavior is kept: Windows and Linux default to
hijackwhenauto-routeis enabled, otherwisedisabled; macOS defaults todisabled
dns-hijack
Section titled “dns-hijack”DNS hijacking. Redirects matched connections into the internal DNS module. If no protocol is specified, it defaults to udp://.
strict-route
Section titled “strict-route”Enforces strict routing rules when auto-route is enabled.
On Linux:
- Makes unsupported networks unreachable.
- Routes all connections to the TUN interface.
It prevents address leaks and allows DNS hijacking to work on Android.
On Windows:
- Adds firewall rules to block DNS leaks caused by Windows’ normal multi-homed DNS resolution behavior.
It may cause certain applications (such as VirtualBox) to malfunction under specific scenarios.
Maximum Transmission Unit. It affects the transfer rate under extreme conditions. General users can leave it at default.
Enable Generic Segmentation Offload. Linux only.
gso-max-size
Section titled “gso-max-size”The maximum length of a data chunk.
inet6-address
Section titled “inet6-address”Specify the IPv6 address of the TUN interface.
udp-timeout
Section titled “udp-timeout”UDP NAT expiration time, in seconds. Default is 300 (5 minutes).
iproute2-table-index
Section titled “iproute2-table-index”The iproute2 routing table index generated by auto-route. Default is 2022.
iproute2-rule-index
Section titled “iproute2-rule-index”The iproute2 rule starting index generated by auto-route. Default is 9000.
endpoint-independent-nat
Section titled “endpoint-independent-nat”Enable Endpoint-Independent NAT. Performance might drop slightly, so it is not recommended to enable it when not needed.
congestion-controller
Section titled “congestion-controller”TCP congestion control algorithm. Available values: cubic, reno, bbr, bbr3. The default value is cubic. Only effective when using the mips stack.
route-address-set
Section titled “route-address-set”Adds destination IP CIDR rules from the specified rule set to the firewall; non-matching traffic will bypass routing.
Linux only, and requires nftables as well as auto-route and auto-redirect to be enabled.
route-exclude-address-set
Section titled “route-exclude-address-set”Adds destination IP CIDR rules from the specified rule set to the firewall; matching traffic will bypass routing.
Linux only, and requires nftables as well as auto-route and auto-redirect to be enabled.
route-address
Section titled “route-address”Routes custom routing subnets instead of the default route when auto-route is enabled. Generally requires no configuration.
route-exclude-address
Section titled “route-exclude-address”Excludes custom subnets when auto-route is enabled.
include-interface
Section titled “include-interface”Restrict routed interfaces. No restrictions by default. Conflicts with exclude-interface, cannot be configured together.
exclude-interface
Section titled “exclude-interface”Exclude interfaces from routing. Conflicts with include-interface, cannot be configured together.
include-uid
Section titled “include-uid”Included users to have their traffic routed by the TUN interface. Users not configured will not have their traffic routed by the TUN interface. No restrictions by default.
include-uid-range
Section titled “include-uid-range”Included user range to have their traffic routed by the TUN interface. Users not configured will not have their traffic routed by the TUN interface.
exclude-uid
Section titled “exclude-uid”Exclude users to prevent their traffic from being routed by the TUN interface.
exclude-uid-range
Section titled “exclude-uid-range”Exclude user range to prevent their traffic from being routed by the TUN interface.
include-mac-address
Section titled “include-mac-address”Restrict routed LAN devices by source MAC address. Linux only; requires auto-route and auto-redirect.
exclude-mac-address
Section titled “exclude-mac-address”Exclude LAN device traffic by source MAC address. Linux only; requires auto-route and auto-redirect.
include-android-user
Section titled “include-android-user”Included Android users to have their traffic routed by the TUN interface. Users not configured will not have their traffic routed by the TUN interface.
| Common User | ID |
|---|---|
| Owner | 0 |
| Second Space | 10 |
| App Cloner | 999 |
include-package
Section titled “include-package”Included Android application package names to have their traffic routed by the TUN interface. Application packages not configured will not have their traffic routed by the TUN interface.
exclude-package
Section titled “exclude-package”Exclude Android application package names to prevent their traffic from being routed by the TUN interface.
Legacy Syntax, Deprecated Soon
Section titled “Legacy Syntax, Deprecated Soon”inet4-route-address
Section titled “inet4-route-address”Routes custom subnets instead of the default route when auto-route is enabled. Generally requires no configuration.
inet6-route-address
Section titled “inet6-route-address”Routes custom subnets instead of the default route when auto-route is enabled. Generally requires no configuration.
inet4-route-exclude-address
Section titled “inet4-route-exclude-address”Excludes custom subnets when auto-route is enabled.
inet6-route-exclude-address
Section titled “inet6-route-exclude-address”Excludes custom subnets when auto-route is enabled.
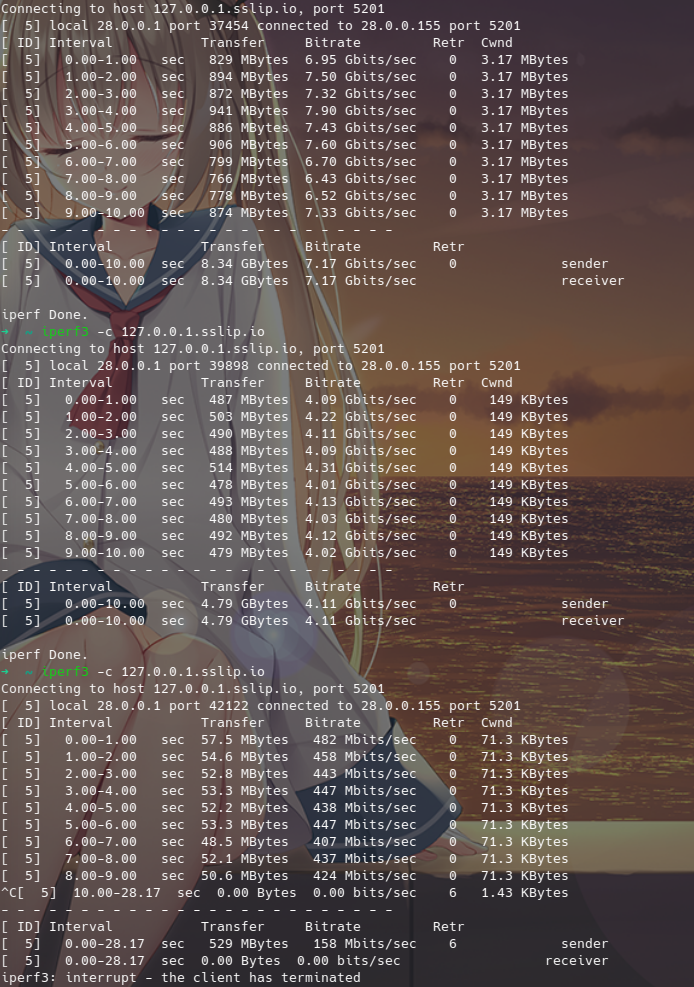
Network Loopback Test for TUN Protocol Stacks
Section titled “Network Loopback Test for TUN Protocol Stacks”From top to bottom are system/gvisor/lwip respectively, for reference only. The platform is Linux; Windows and MacOS may vary.